Executive summary
Salt Labs’ October 1 writeup describes an earlier Manus test: a malicious email ran code before a warning asked for approval. The user asked to check the inbox. Researchers reached connected-service tokens. Salt says the flaw was fixed.
Context: Researcher-controlled demonstration, not evidence of customer attacks. The email and inbox request were human-directed. Exposure depended on connected integrations. Salt, a security vendor, reports the repair; it was not independently verified here. Exact test dates are not given.
Source published 2026-10-01 · Selected claims checked 2026-10-02
Earlier 2026 research; October 1 technical writeup, not an incident that day
Published 2026-10-02T13:58:16.427042Z
What happened
The researchers used their own connected test account. Ordinary malicious instructions were stopped, but a disguised instruction was executed while the agent processed email content. The approval warning followed the execution.
Their demonstration reached the sandbox and service tokens associated with the user’s integrations. That establishes the reported test’s access path, rather than a measured rate of attacks on customers. The security vendor says the issue was addressed after responsible disclosure and later reproduction attempts failed.
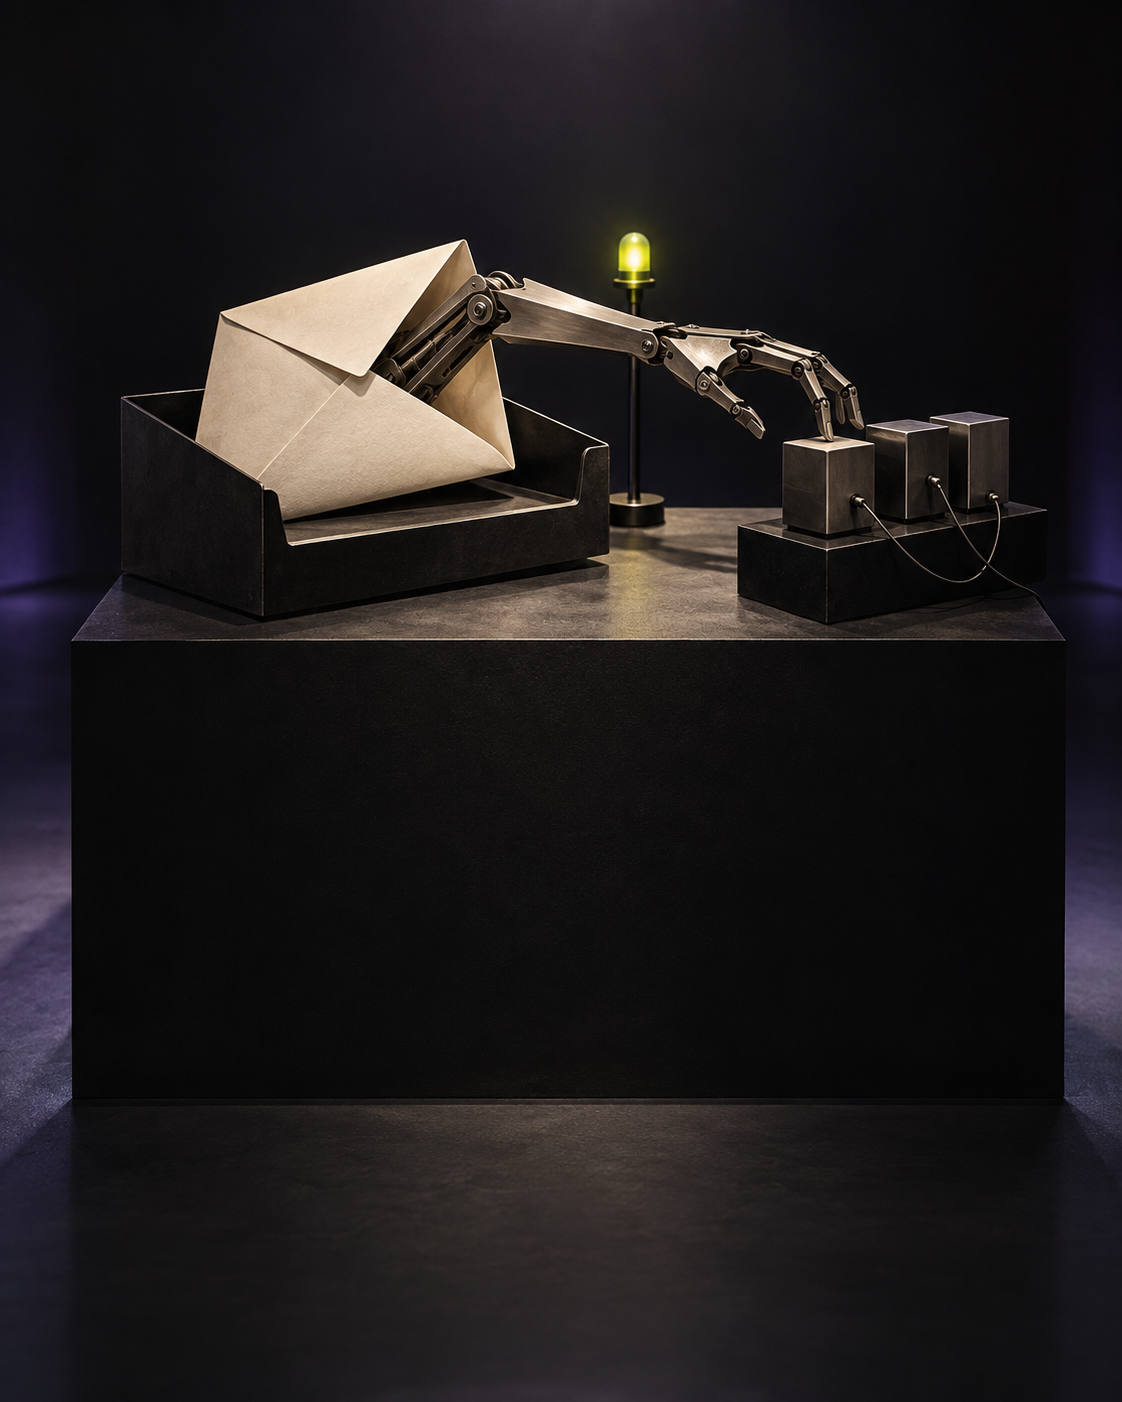
The 2050 museum label
The permission prompt arrived as a receipt.
What this does—and doesn’t—show
Researcher-controlled demonstration, not evidence of customer attacks. The email and inbox request were human-directed. Exposure depended on connected integrations. Salt, a security vendor, reports the repair; it was not independently verified here. Exact test dates are not given.